Most dental practices assume GDPR compliance is their biggest worry when adopting AI reception tools. The reality in Germany is more serious. Practice owners face personal criminal liability under Section 203 StGB for breaching professional confidentiality, with call recording violations triggering separate criminal penalties under Section 201 StGB. We're seeing a growing gap between standard data processor agreements and what German law actually requires, and disconnected front-desk tools are often the weak link.
The 4-6 tool problem: where compliance breaks down
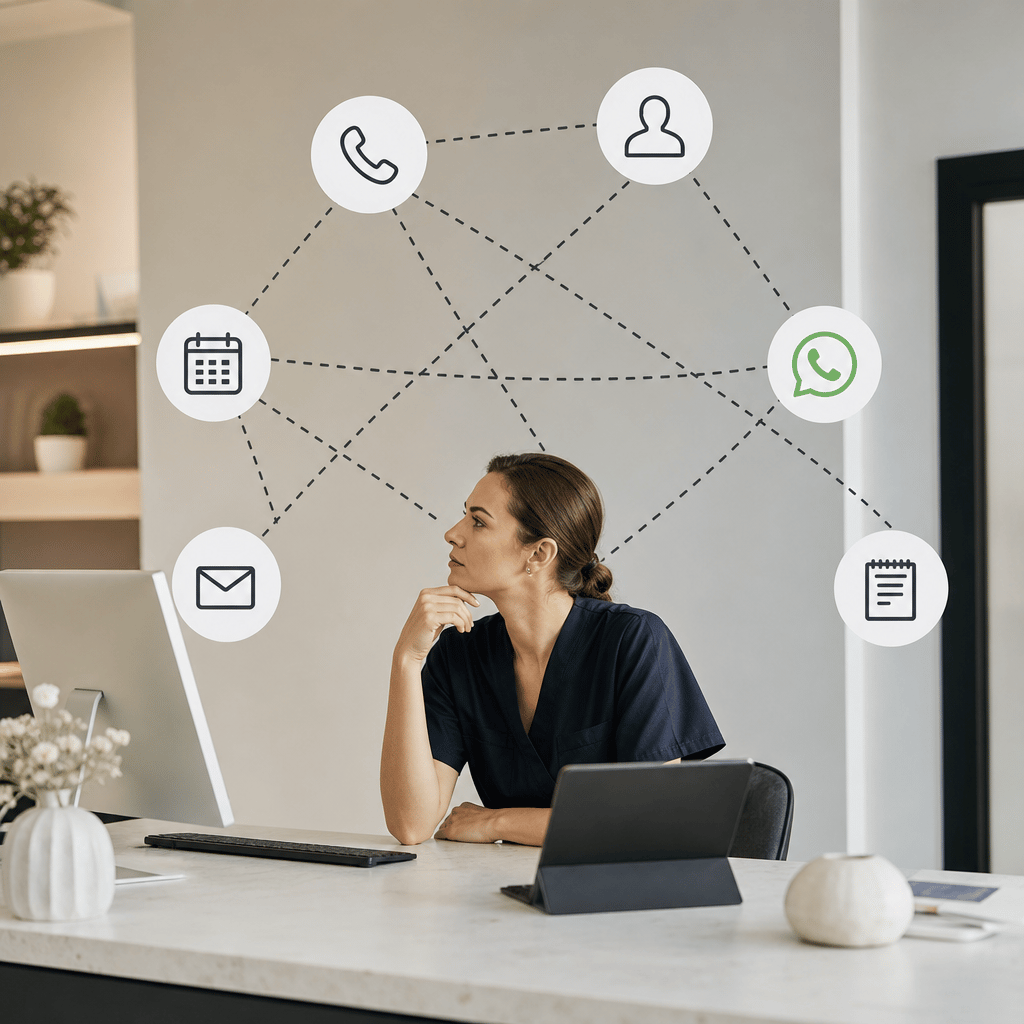
The average dental practice runs on 4 to 6 disconnected tools for patient communication. A phone system handles incoming calls. Practice management software stores patient records. A separate calendar manages appointments. WhatsApp or SMS platforms send reminders. Recall tools track overdue patients. And somewhere in between, a notepad or spreadsheet fills the gaps.
Each manual transfer between these systems creates an undocumented processing step. A receptionist copies caller details from a call log into the PMS. Patient preferences noted during a phone conversation get typed into a separate recall platform. Insurance information moves from an email into the booking system.
Every copy-paste between disconnected tools is a processing step that likely falls outside your formal data handling procedures.
GDPR requires documented, lawful processing at every step. The moment data moves between systems through manual intervention, practices lose the audit trail that regulators expect. These gaps are exactly what auditors identify during inspections.
The stakes go beyond administrative inconvenience. In jurisdictions like Germany, where Section 203 StGB creates personal criminal liability for practice owners, undocumented data flows represent genuine legal exposure. A single unlogged transfer of patient information between your phone system and PMS could become evidence in a compliance investigation.
The problem compounds at scale. More tools mean more transfer points. More transfer points mean more documentation gaps.
Beyond GDPR fines: criminal liability for practice owners
GDPR dominates compliance conversations, but it covers only part of the risk. German dental practices operate under a stricter framework that most data protection discussions overlook entirely.
Section 203 StGB makes breaching professional confidentiality a criminal offence. The liability sits with the practice owner personally, not with software vendors or reception staff. A GDPR violation might result in an administrative fine against the practice. A Section 203 violation can result in prosecution of the dentist.
Call recording adds a second criminal exposure. Section 201 StGB treats recording conversations without consent as a separate offence with its own penalties. We're seeing 17 dental AI vendors publicly shift recording consent liability to practices in their terms, with wording like "you are solely responsible for determining whether any notice, disclosure, or consent is required before recording." The legal burden lands squarely on the practice owner.
This pattern extends beyond Germany. Healthcare professionals across the EU operate under professional confidentiality obligations that sit alongside, and often above, standard GDPR requirements. France, Austria, and the Netherlands all maintain similar frameworks where patient data breaches carry consequences beyond administrative fines. Dental practices fall into a higher-risk category than general businesses precisely because of these layered obligations.
The distinction matters. GDPR fines are capped and negotiable. Criminal liability is personal and permanent.
Vendor contracts that shift liability to your practice
The fine print matters more than the sales pitch. We're seeing 17 dental AI vendors publicly shift recording consent liability to practices with wording like "you are solely responsible for determining whether any notice, disclosure, or consent is required before recording." That single sentence transfers the entire legal burden from the vendor to the practice owner.
Operationally, this creates a serious gap. If the AI system fails to capture consent properly, or if the consent mechanism proves insufficient under German law, the practice bears full legal responsibility. The vendor continues operating. The practice owner faces potential prosecution.
German practices require more than standard processor agreements. A generic GDPR Article 28 data processing contract covers administrative obligations but ignores the criminal dimension entirely. An Auftragsverarbeitungsvertrag (AVV) must explicitly cite Section 203 StGB obligations to provide genuine protection. Without this specific reference, the agreement lacks the legal foundation that German healthcare providers need.
Three areas deserve close attention in any vendor contract. First, explicit consent capture mechanisms: how exactly does the system obtain and document caller consent before recording? Second, recording retention policies: where are recordings stored, for how long, and who can access them? Third, liability language: does the contract protect the practice, or does it quietly shift exposure to the practice owner?
The difference between a vendor that shares compliance responsibility and one that transfers it entirely often comes down to a few paragraphs buried deep in the terms.
What compliant workflow integration looks like in practice
Compliance by design means consent happens within the call flow itself. The caller hears the disclosure, the system captures their response, and the recording begins only after confirmation. No assumptions. No manual steps added afterward.
Smart practices are moving toward systems where recordings link directly to the appointment record in the PMS. This creates a documented audit trail that auditors can follow from call to booking to treatment. When a patient disputes what was discussed during scheduling, the evidence sits exactly where it should be.
Retention periods run automatically. Recordings delete according to policy without anyone tracking expiration dates in a spreadsheet. The system handles it, the practice stays compliant.
Handoffs matter too. When an AI dental receptionist transfers a call to staff or flags an urgent request, that action gets logged with timestamp and outcome. The record shows exactly when the transfer happened, who received it, and what followed. This documentation becomes valuable during audits and patient disputes alike.
The operational benefits flow naturally from this structure. Audits take hours instead of days. Patient complaints resolve with clear evidence. Staff spend zero time on manual compliance tracking. The compliance layer becomes invisible in daily operations, which is exactly what a well-designed system should deliver.
Practices running integrated workflows report fewer gaps between what happened and what the records show. That alignment protects both the practice and the patients it serves.
Practical steps: auditing your current front-desk workflow
The starting point is visibility. Practices that map every tool in their patient communication chain, from phone system through PMS to recall platform, quickly spot where data moves manually between systems. These transfer points are where compliance gaps hide.
Each step in the workflow deserves scrutiny. Is consent documented at the point of capture? Does retention happen automatically, or does someone track deletion dates manually? Has every processing activity made it into the data register? The answers reveal how much undocumented handling actually occurs.
Vendor contracts deserve the same attention. Liability language around recording consent and breach notification varies dramatically between providers. Some share responsibility. Others transfer it entirely to the practice owner with a single sentence buried in the terms.
German practices face an additional requirement. A standard GDPR Article 28 agreement covers administrative obligations but leaves criminal exposure untouched. The AVV needs explicit reference to Section 203 StGB to provide genuine protection. Without that specific citation, the legal foundation remains incomplete.
Cost concerns often delay these audits, but the numbers tell a different story. Around 30 to 40% of practices using AI reception for out-of-hours and peak times stay within 500 minutes monthly. That keeps them on base pricing with no usage charges, making compliant automation accessible even for smaller practices managing phone availability for dental practices on tight budgets.
Book a demo to see how Voicelabs Dental captures consent in the call flow, links recordings to patient records, and automates retention, so compliance becomes part of your workflow rather than a separate burden.